
Deep Packet Inspection Software & Libraries
Identify the application behind every flow
Deep packet inspection (DPI) identifies the application behind each flow, even when traffic is encrypted.
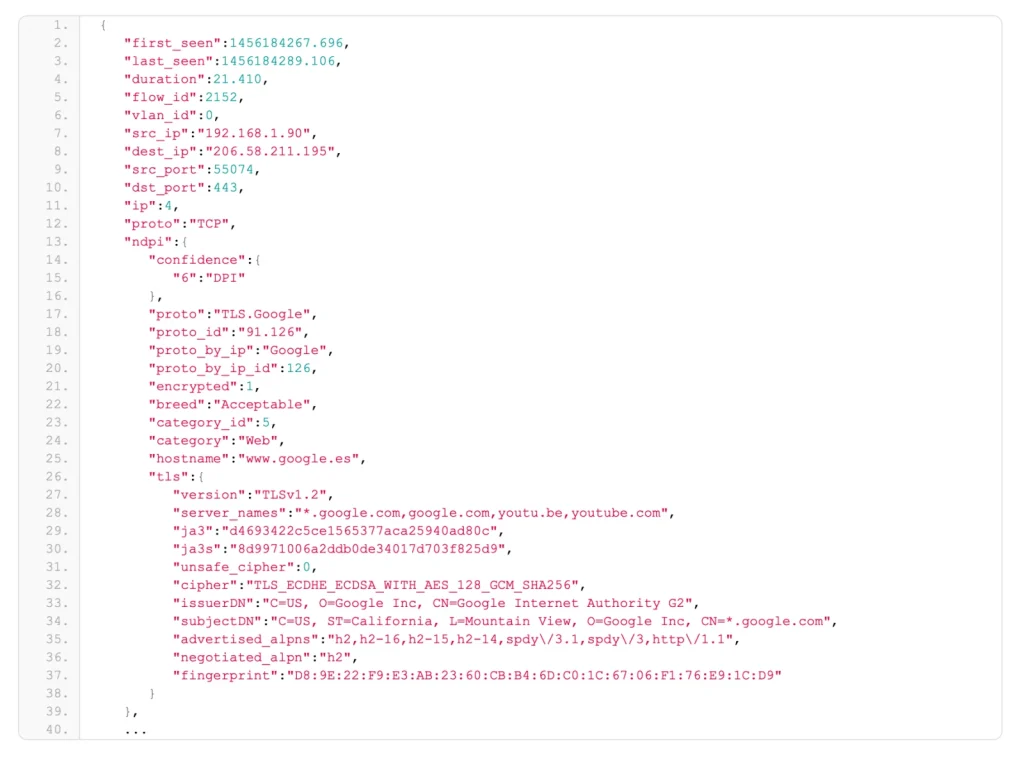
nDPI is the open source DPI library developed by ntop. It is released under the LGPL, detects hundreds of Layer-7 protocols and extracts metadata such as TLS certificates and fingerprints.
Guide
TLS fingerprinting
Learn how nDPI helps with TLS fingerprinting (JA3 and JA4).
Why use nDPI for deep packet inspection?
nDPI is the open source deep packet inspection library used by ntopng and nProbe. It recognizes 450+ protocols and applications, including encrypted traffic, using metadata such as TLS fingerprints and DNS, without decrypting the payload. Because it is open source, the same detections follow you across the ntop products and your own tools.
Get started
Not sure which one to choose?
Download the free Community edition, compare editions and buy in the shop, or talk to the ntop team about your requirements.
