
DDoS Mitigation Software
Filter attack traffic at line rate
DDoS attacks flood links and services with unwanted traffic.
nScrub is a DDoS mitigation system based on PF_RING ZC. It operates at 10+ Gbit on commodity hardware and scales to terabit capacity with a modular architecture.
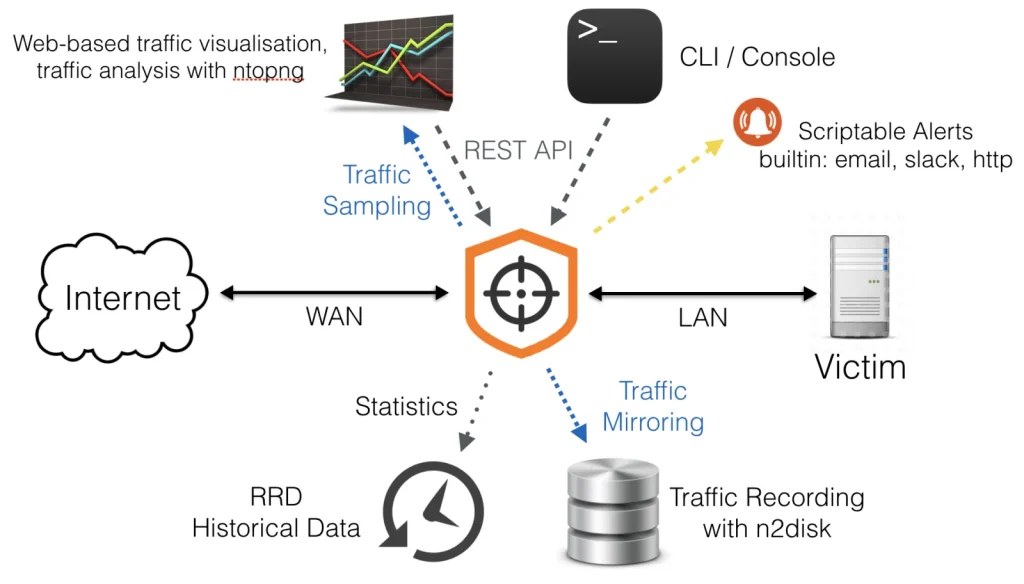
Deployment
How nScrub is deployed
- Transparent bridge (bump in the wire): traffic passes untouched until an attack is detected, then mitigation starts automatically.
- Router mode with BGP diversion: divert and clean only the traffic under attack, on demand.
When do I need DDoS mitigation?
nScrub filters volumetric attack traffic at line rate at the network edge, so service stays available without waiting on upstream mitigation. It fits ISPs, hosting providers and data centers that must protect many customers on shared links, and it works alongside ntopng and nProbe for visibility into the attack.
Get started
Not sure which one to choose?
Download the free Community edition, compare editions and buy in the shop, or talk to the ntop team about your requirements.
