
Feature
Application visibility with deep packet inspection
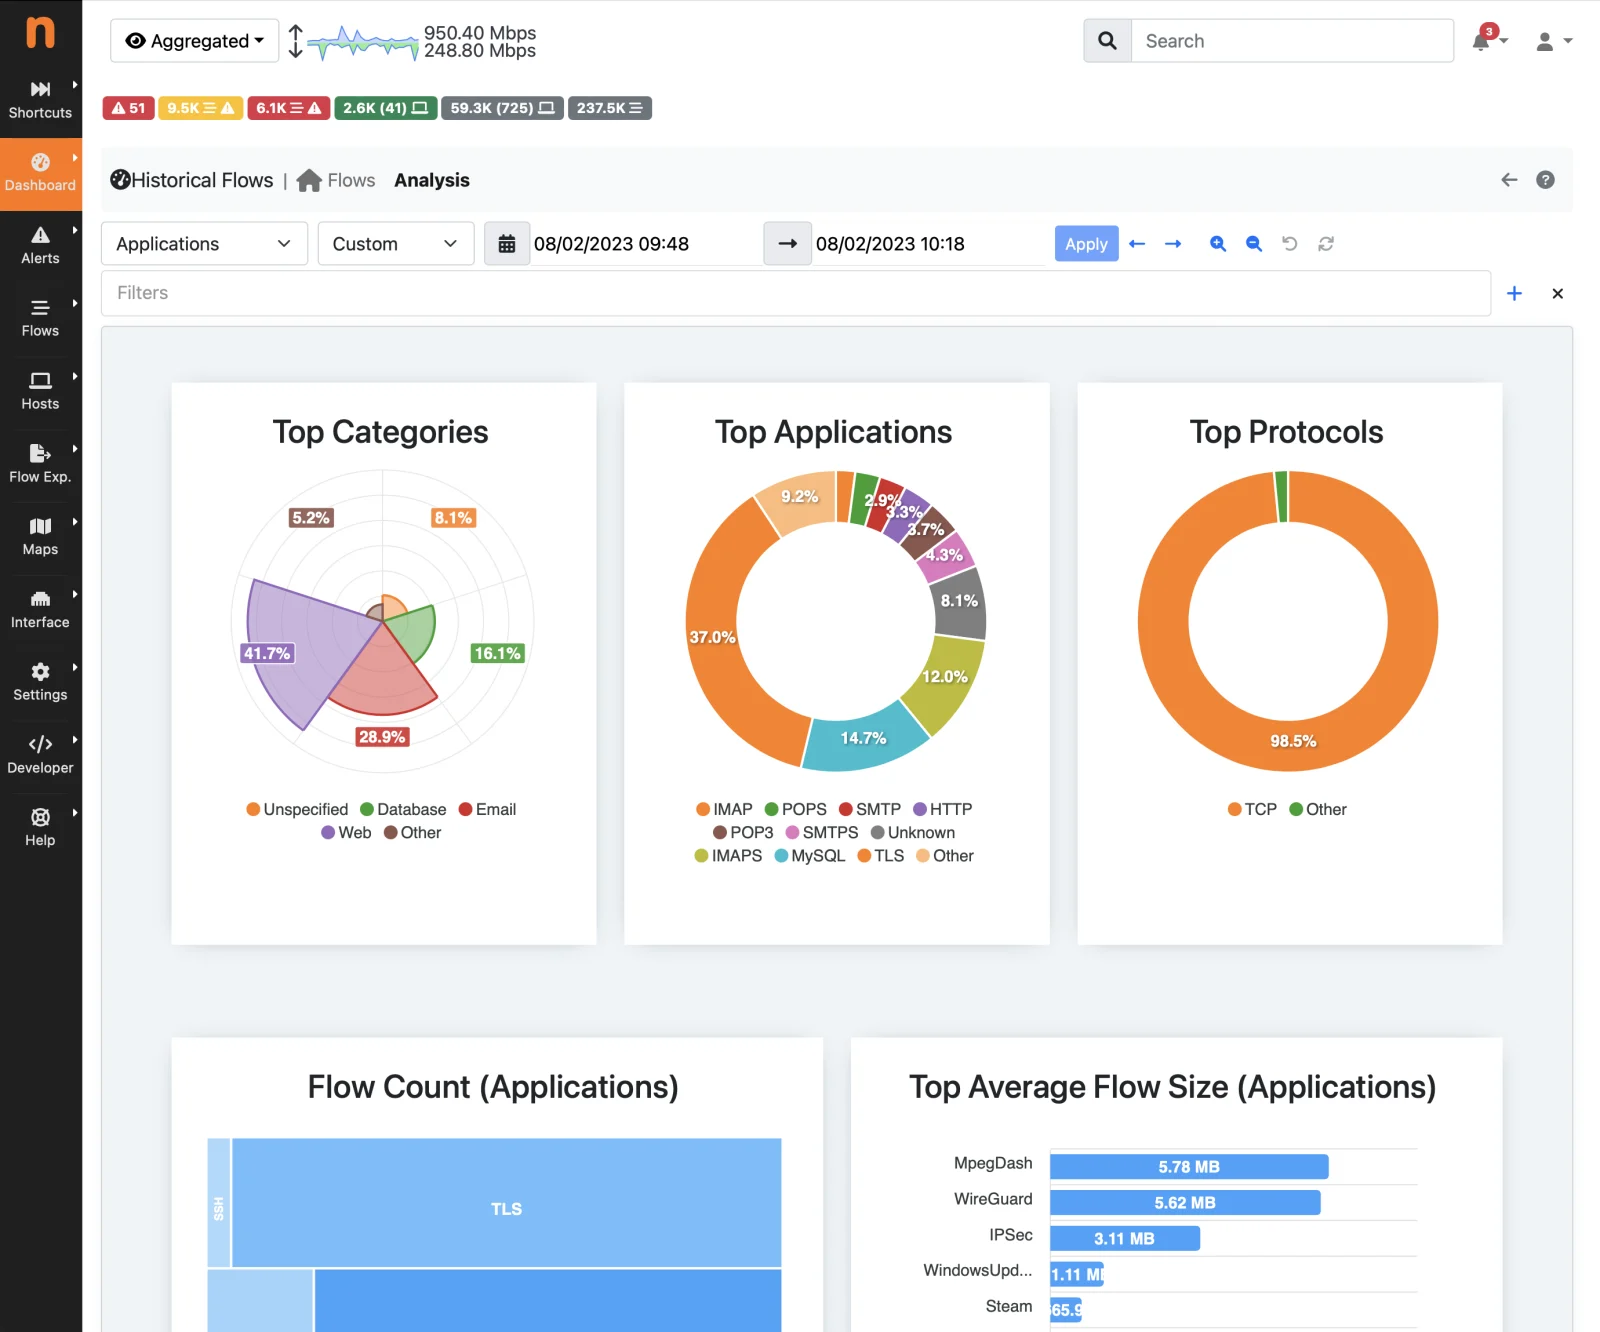
nDPI, the open source deep packet inspection library from ntop, recognises 450+ protocols and applications, including encrypted traffic, so you see what runs on your network and not just the port number.
Capabilities
What you can see
450+ protocols and applications
Identify apps like Teams and Netflix even when they all use port 443.
Encrypted traffic metadata
TLS, JA4 fingerprints and DNS metadata describe encrypted flows without decrypting them.
Flow risks
Suspicious and misconfigured flows are flagged automatically in ntopng.
Open source
nDPI is open source and used by ntopng and nProbe, so the detections follow you across products.
Use cases
When teams use it
Security investigations
Combine application, fingerprint and risk data to prioritise suspicious hosts.
FAQ
Frequently asked questions
Is nDPI really open source?
Yes. nDPI is an open source deep packet inspection library, and it powers ntopng and nProbe.
Can it inspect encrypted traffic?
It extracts TLS metadata such as JA4 fingerprints and SNI, which identify most applications without decrypting the payload.
Are TLS fingerprints enough to detect malware?
No. They are one signal. Combine them with destination reputation, behavior and flow risks.
Get started
See your applications clearly
Download the free Community edition of ntopng, or talk to the ntop team about your requirements.
