
with zero-copy drivers
source
and Zeek ready
The recommendation
Who should choose PF_RING
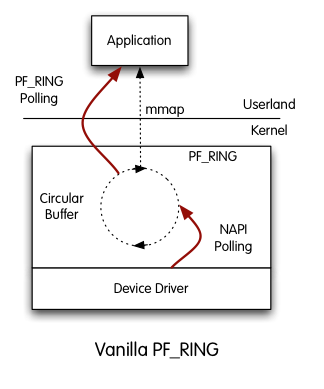
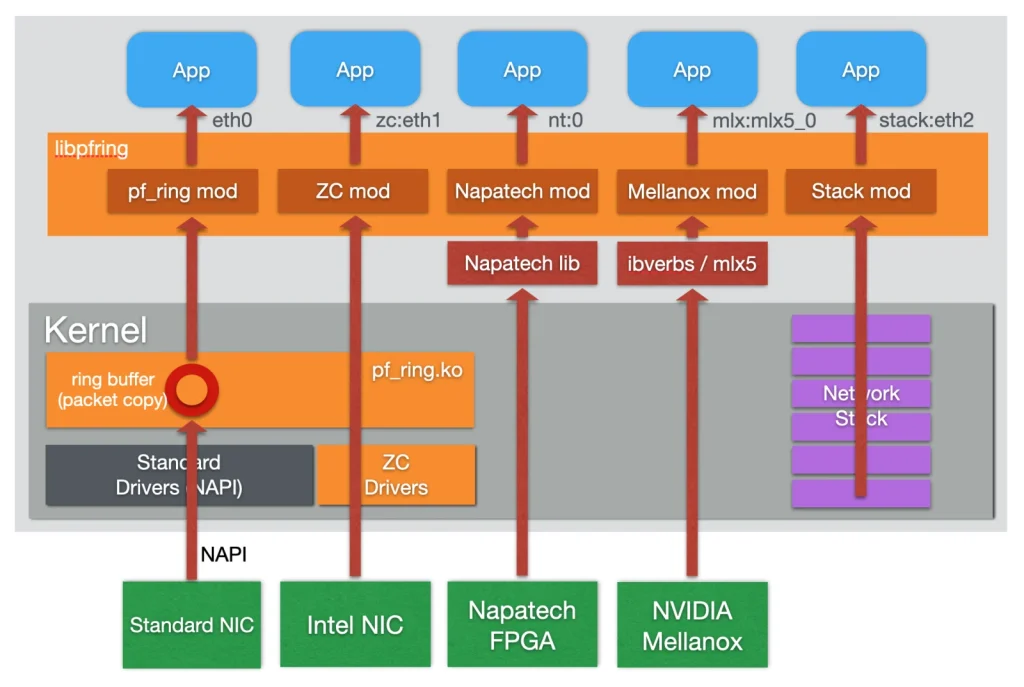
PF_RING is an open source packet capture framework for Linux that speeds up capture and transmission on any adapter. Choose it when libpcap loses packets, or when tools such as Suricata, Zeek, ntopng or n2disk must keep up with multi-gigabit traffic.
- You lose packets on busy links with standard capture.
- You run Suricata or Zeek and need fast, load-balanced capture.
- You need PCAP replay and traffic generation for lab testing.
The ideal use case
Ideal use case for PF_RING
- Environment: Linux servers capturing network traffic, in monitoring, IDS/IPS and test labs.
- Team: network engineers and developers using the C API or libpcap-based tools.
- Technical requirements: no kernel patching; a module is loaded through DKMS. Works on any adapter.
- Problem solved: minimal packet loss at multi-gigabit speed, with filtering (nBPF) and load balancing.
Ideal for Every Environment
Deployment scenarios
Packet Capture Acceleration
PF_RING dramatically enhances packet capture performance, making it ideal for building scalable network monitoring solutions. Whether for flow analysis, traffic accounting, or deep packet inspection, PF_RING ensures minimal packet loss even at multi-gigabit speeds, and above 100 Gbit with zero-copy drivers.
Inline Applications
Security tools like Suricata and Zeek integrate seamlessly with PF_RING to process high-speed traffic efficiently. This enables real-time threat detection and mitigation without sacrificing packet capture accuracy or system performance.
Traffic Replay and Generation
PF_RING enables accurate PCAP traffic replay and high-performance synthetic traffic generation for lab testing, benchmarking, and QA environments. It allows teams to emulate real-world conditions and validate the behavior of network appliances, security systems, and applications under controlled scenarios.
The alternatives
PF_RING alternatives, compared
Same criteria for each option: role, when to choose it, limits and cost.
PF_RING ZC
- Role: Zero-copy drivers for 100+ Gbit line rate and the lowest CPU usage.
- Choose it when: You need line rate at any packet size or zero-copy between processes and VMs.
- Limits: Licensed per adapter family, x86 64-bit.
- Cost: from 49.95 euro
PF_RING FT
- Role: Flow table and Layer-7 classification on top of capture.
- Choose it when: You build a flow probe or an IDS accelerator.
- Limits: Licensed.
- Cost: 199.95 euro
The tradeoffs
When PF_RING is not the right choice
- Vanilla PF_RING does not reach line rate at 100 Gbit: that needs PF_RING ZC.
- It is Linux only.
- It is a capture layer. You still need an application on top, such as ntopng, nProbe or n2disk.
The proof
Specifications, versions, pricing and documentation
Features, supported platforms and protocols, editions with prices, documentation links and answers to common questions follow below.
at a glance
Key Features
- Linux network socket available for all kernels (latest kernels for the most common Linux distributions are officially supported)
- DKMS support and no need to patch the Linux kernel (a kernel module is automatically loaded)
- Agnostic API for device driver independent application code
- Kernel-based packet capture for all adapter models
- Libpcap support for seamless integration with existing pcap-based applications
- Optimized nBPF filters in addition to the legacy BPF
Enable PF_RING Zero-Copy for line-rate performance!
PF_RING ZC drivers implement Zero-Copy packet capture and transmission for performance at 100+ Gbit/s and the lowest CPU overhead, in addition to enhanced offloads (filtering, timestamping, load-balancing, ...).
models
Choose Your Model
Already included in all ntop applications.
Open Source
- Kernel-based acceleration
- Support for all Network adapters
- Packet headers parsing
- Kernel-based clustering and load-balancing
- In-kernel software filters and BPF
- Source code available on GitHub
Specifications
Tech Specs
FAQ
Frequently Asked Questions
What is PF_RING?
A packet capture framework that accelerates capture and transmission on any adapter, with packet parsing, filtering and load balancing.
Do I need PF_RING ZC?
Use ZC (zero copy) for 100 Gbit line rate processing and for delivering packets between processes and virtual machines.
Does PF_RING work with Suricata and Zeek?
Yes. Both integrate with PF_RING to process high-speed traffic with minimal packet loss.
Which ntop tools use PF_RING?
ntopng, nProbe, n2disk and nScrub rely on PF_RING for fast capture.
Related
Keep exploring
Pricing and editions
Compare editions and ways to buy.
Solutions
By use case and industry.
User guide
Installation and configuration.
Get started
Ready to see it on your network?
Download the free Community edition, compare editions and buy in the shop, or talk to the ntop team about your requirements.
